HackTheBox - Takeoff
Writeup pending - this machine hasn't retired on HackTheBox yet.
[email protected]:~$ whoami
Rahul R · Security Engineer · Penetration Tester
Dubai, UAE
[email protected]:~$ cat interests.txt
pentesting · active directory · cloud · android
reverse engineering · malware · hardware · ctf
[email protected]:~$ ls -la blog/
 19  posts          5  htb-writeups
  9  categories    44  tags
[email protected]:~$ htb --status
Elite Hacker · #85 global · 1774 pts · 258/242 owns
[email protected]:~$ ▍Writeup pending - this machine hasn't retired on HackTheBox yet.
Writeup for the Shelter Bank Heist event at GISEC 2026 - LDAP injection in a bank's support lookup leaks a domain user, a BloodHound gMSA edge turns that into jump-server admin, a ligolo-ng pivot opens the firewalled parent domain, and an ESC8 NTLM relay through a hijacked SMB port into AD CS web enrollment ends with a SIDHistory golden ticket, a parent-domain DCSync, and a settled $10M transfer.
Writeup for Cold Storage, a 4-flag Cloud/AWS challenge from Dubai Cyber Challenge 2026 - chaining an open Cognito signup, a homegrown path-traversal filter, a client-editable authorization attribute, and SSRF to IMDS into full IAM credential theft and a KMS-protected flag.
Writeup for Data Portal, a Cloud/AWS challenge from Dubai Cyber Challenge 2026 - an unauthenticated SSRF proxy chained through ECS task metadata into a public ECR image pull.
Writeup for Lost Luggage, a Cloud/AWS challenge from Dubai Cyber Challenge 2026 - chaining a debug endpoint leak into a direct, unauthenticated S3 read that bypasses the app's own access control.
Writeup pending - this machine hasn't retired on HackTheBox yet.
Writeup pending - this machine hasn't retired on HackTheBox yet.
Writeup pending - this machine hasn't retired on HackTheBox yet.
Writeup pending - this machine hasn't retired on HackTheBox yet.
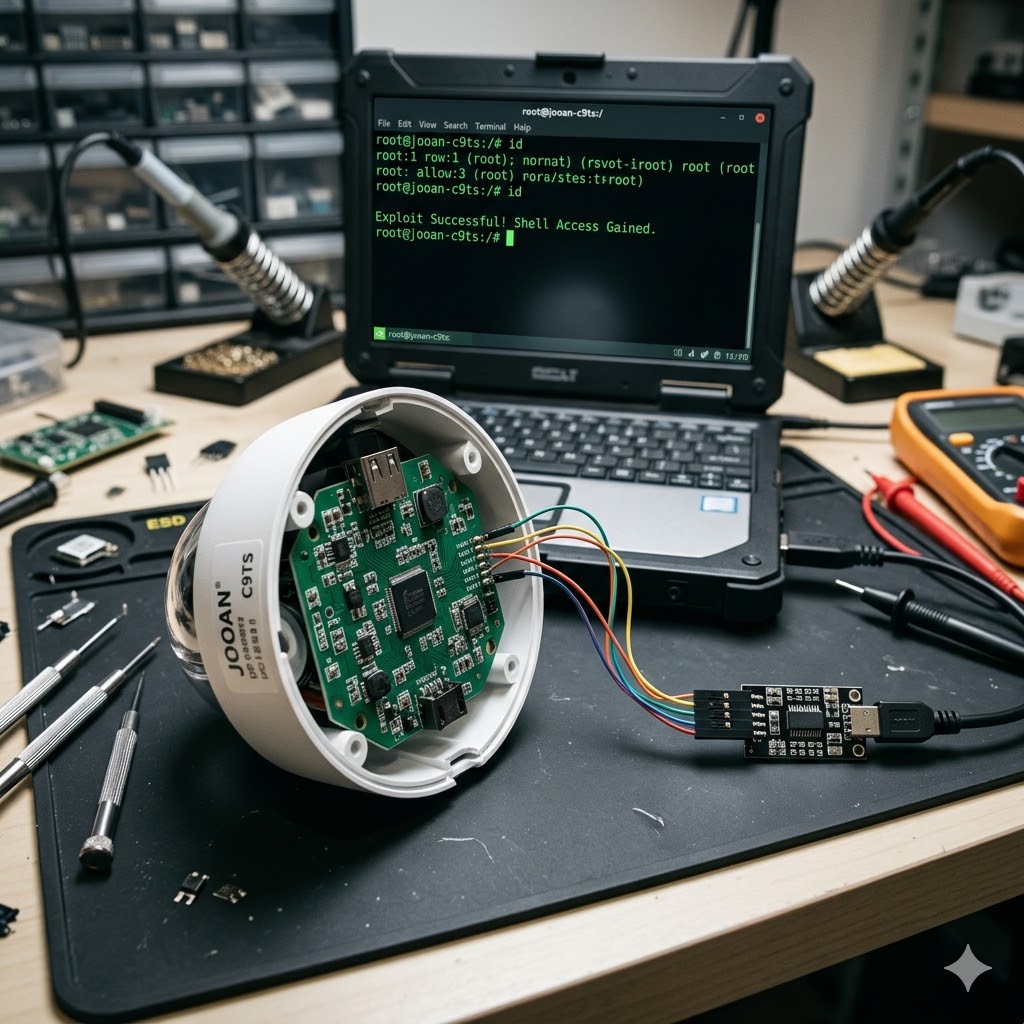
How a cheap IP camera and some 'procrastination' led to a full Remote Code Execution vulnerability.
Technical Walkthrough on solving the TokenBleed challenge from MobileHackingLabs
In this post, I reverse engineer a real-world Android malware campaign targeting SBI bank customers, uncovering how attackers use APK droppers to deploy SMS-hijacking trojans.
Creating Speed Hack and Super Jump on Pwn Adventure 3 using Cheat Engine
Creating God Mode and One Hit Kills on Pwn Adventure 3 using Cheat Engine
This is the walkthrough for the newly introduced challenge category GamePWN on HackTheBox
Ra is a windows machine which starts with a typical business website for Windcorp where there is a password reset function which can be used to change a user's password to gain access to a SMB share to download spark live chat application which is vulnerable that can be used to harvest a user's NTLM hash that can be used to gain initial access to the machine.On further exploring the machine a script can be seen that contains a username who's password can be changed since the user has extended rights to change password as he is a member of the account operator group.Analysing the script we can see that there is command injection vulnerability that can be abused to gain admin privilege and pwn the machine
Here is a short write-up on an interesting bug that I found while testing a site where I was able to chain multiple IDORs to execute Code on the server
This is the walkthrough for the challenges that were provided as a part of COCON's DomeCTF
This is the walkthrough for the challenges that were provided as a part of Sector443's CTF